The Language of Emojis in Threat Intelligence: How Adversaries Signal, Obfuscate, and Coordinate Online
Blogs Blog In this post, we examine how threat actors use emojis across illicit communities, how these symbols function...
Blogs Blog In this post, we examine how threat actors use emojis across illicit communities, how these symbols function...

On March 30-31, 2026, threat actors published two malicious versions of the popular HTTP library axios (versions 1.14.1 and...

Threat actors with ties to Iran successfully broke into the personal email account of Kash Patel, the director of the...

Ravie LakshmananMar 27, 2026Ransomware / Malware Threat actors are using adversary-in-the-middle (AitM) phishing pages to seize control of TikTok for...
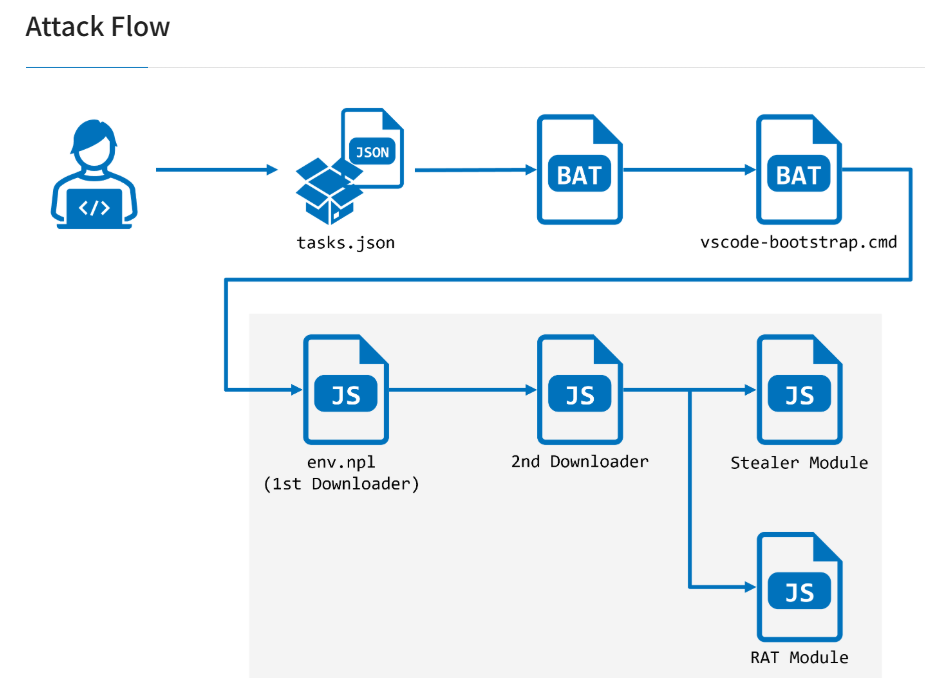
North Korea-linked threat actors abuse VS Code auto-run to spread StoatWaffle malware Pierluigi Paganini March 24, 2026 North Korea-linked threat...

The North Korean threat actors behind the Contagious Interview campaign, also tracked as WaterPlum, have been attributed to a malware...
Iran-linked actors use Telegram as C2 in malware attacks on dissidents Pierluigi Paganini March 23, 2026 Iran-linked actors use Telegram...

Ravie LakshmananMar 23, 2026Vulnerability / Endpoint Security Threat actors are suspected to be exploiting a maximum-severity security flaw impacting Quest...
Russia-linked actors target WhatsApp and Signal in phishing campaign Pierluigi Paganini March 22, 2026 Russia-linked actors target WhatsApp and Signal...

Ravie LakshmananMar 21, 2026Cyber Espionage / Threat Intelligence Threat actors affiliated with Russian Intelligence Services are conducting phishing campaigns to...

Ravie LakshmananMar 21, 2026Malware / Threat Intelligence The threat actors behind the supply chain attack targeting the popular Trivy scanner...
EU sanctions Chinese and Iranian actors over cyberattacks on critical infrastructure Pierluigi Paganini March 17, 2026 EU sanctions Chinese and...

Ravie LakshmananMar 17, 2026Threat Intelligence / Endpoint Security North Korean threat actors have been observed sending phishing to compromise targets...
Following initial access, the threat actors conducted extensive lateral movement using a combination of legitimate administration tools and credential abuse....

Ukrainian entities have emerged as the target of a new campaign likely orchestrated by threat actors linked to Russia, according...