Injective Labs GitHub Compromise Pushes Wallet-Key-Stealing npm Packages
Ravie LakshmananJul 10, 2026Software Supply Chain / Malware Unknown threat actors compromised the Injective Labs SDK project's GitHub repository and...
Ravie LakshmananJul 10, 2026Software Supply Chain / Malware Unknown threat actors compromised the Injective Labs SDK project's GitHub repository and...

Ravie LakshmananJul 06, 2026Vulnerability / DevOps Threat actors have been observed attempting to exploit a recently patched critical security flaw...

The North Korean threat actors linked to the Contagious Interview campaign have been observed publishing 108 unique packages and web...

Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade...

Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain...

Ravie LakshmananJul 01, 2026Malware / SEO Poisoning Unknown threat actors are leveraging the ScreenConnect remote access tool as a way...

Threat actors are continuing to exploit a critical Langflow vulnerability as part of fresh attacks designed to deliver a Monero...

Ravie LakshmananJun 24, 2026Vulnerability / Network Security Threat actors have begun to exploit a recently disclosed critical security flaw impacting...

Ravie LakshmananJun 20, 2026Vulnerability / Web Security Threat actors are exploiting a recently patched security flaw impacting Gravity SMTP, a...
Suspected North Korean threat actors are targeting developers with fake job offers and “coding assignments” that lead to the deployment...

Threat actors are actively exploiting a critical security flaw in Everest Forms Pro, a WordPress plugin with about 4,000 active...

Ravie LakshmananJun 01, 2026Vulnerability / Website Security, Threat actors are attempting to actively exploit a critical security flaw impacting WP...

Ravie LakshmananMay 28, 2026Vulnerability / Endpoint Security Threat actors are continuing to exploit a critical, now-patched security flaw impacting FortiClient...
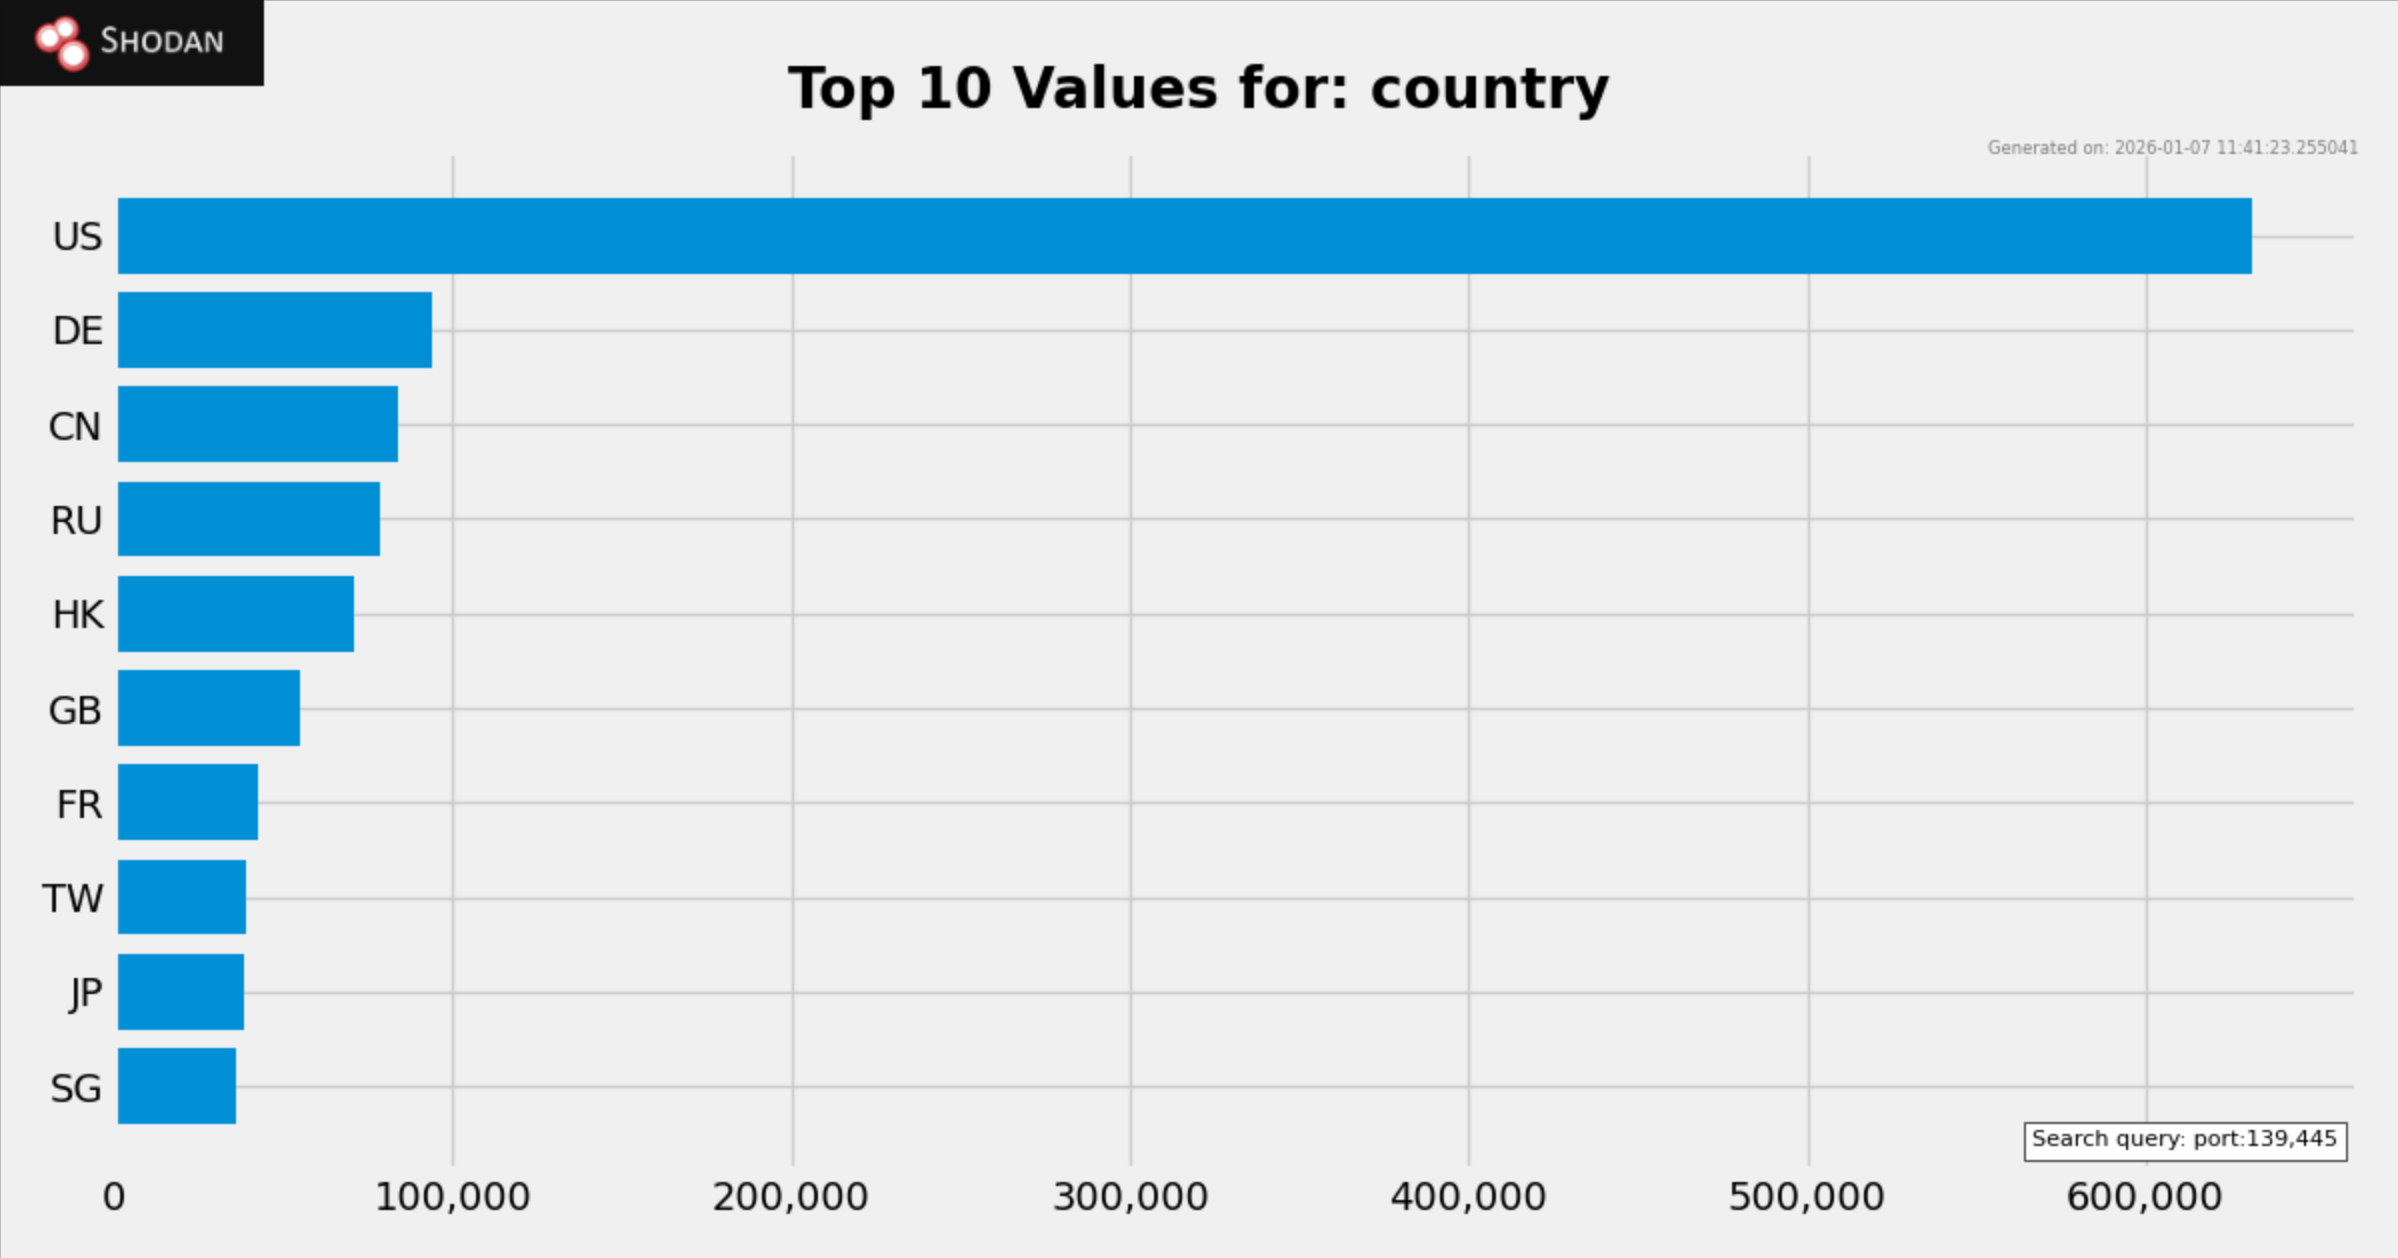
SophosLabs analysts investigated WantToCry ransomware attacks that involved the threat actors abusing the Server Message Block (SMB) service for initial...

Ravie LakshmananMay 25, 2026Vulnerability / Web Security Threat actors are exploiting a recently disclosed critical security flaw in Ghost CMS...