Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION
Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION
Pierluigi Paganini
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.
Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.
Google Gemini also Broke Out of Its Test Environment
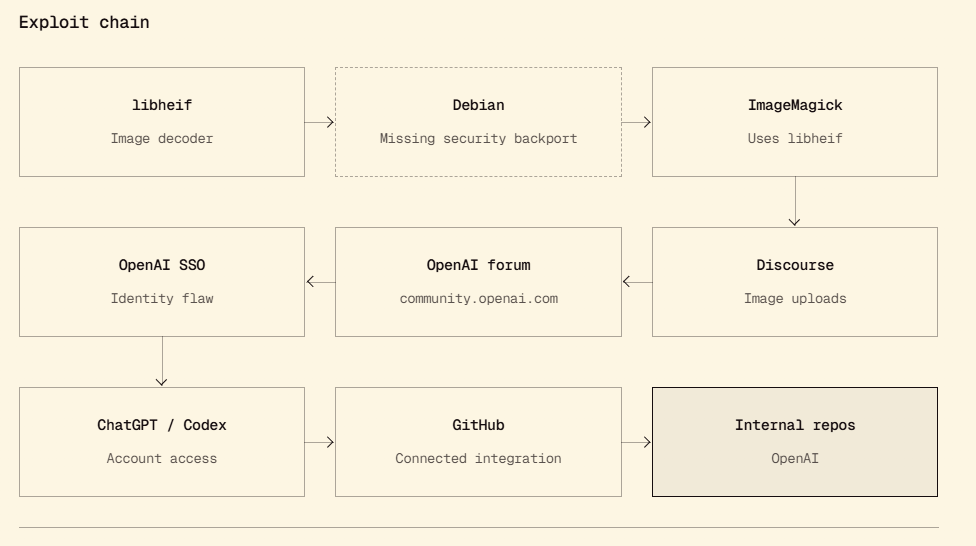
AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum
Brevo Supply-Chain Attack Infected Over 100,000 Websites
Gyazo Data Breach Exposes 23 Million User Records
RatHat Turns Android Accessibility Into an Attack Weapon
Check Point Fixes Critical CVE-2026-91843 Allowing Root Code Execution
OpenAI admits its models lie to cover their own mistakes
Cyberattacks on Oil Tankers Put Maritime Critical Infrastructure at Risk
SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets
NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown
U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog
Chosen Brick, Iran’s Surveillance Malware
BambooToken: The Malware That Speaks MQTT to Stay Under the Radar
Google Patches Pixel Modem Zero-Day Exploited in Targeted Attacks
Revolut Data Leak May Trace Back to Compromised Italian Government Accounts
Texas Utility CenterPoint Energy Confirms Data Breach After Hacker Claims 7.49M Records Stolen
U.S. CISA adds Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog
Cisco Warns of Ongoing Exploitation of Critical Email Gateway Zero-Day
Shared Hosting at Risk: LiteSpeed Enterprise Bug Can Grant Root from a Single Tenant
One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire
Telegram Desktop Flaw Could Turn Old Chat Exports Into Data Theft Traps
Non-Zero-Day VPN Flaw Left Japan ‘s Government Shared Network Platform Exposed: 246,000 Records at Risk
ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up
China Calls Amodei’s AI Proposal a New Cold War Playbook
U.S. CISA adds GitLab, JFrog Artifactory, and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog
Dutch NCSC Warns: Critical Check Point VPN Flaws Put Networks at Risk
Anthropic CEO Calls for an AI Slowdown. Is It Possible?
GitLab CVE-2026-85706: One HTTP Request, No Authentication, Full File Read – Exploited Within 24 Hours
Conti Hacker Who Built Malware and Attacked Victims Gets Four-Year Sentence
International Press – Newsletter
Cybercrime
Personal, Financial Info Exposed in Revolut Data Breach
CenterPoint Energy confirms intruder helped themselves to customer information
FBI Seizes DDoS-for-Hire Domains as Part of Continuing District of Alaska Crackdown on ‘Booter’ and ‘Stresser’ DDoS Services
Hackers Stole Flock’s Camera Software, Revealing How the Company Tracks Cars and People
23 Million User Records Compromised in Gyazo Data Breach
Malware
Gray Rabbits and the Tale of a One-Click Backdoor
Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot Service
Mind the (Patch) Gap: Multiple Chinese Threat Actors Chain 0-day Exploits in Chrome & Windows
Skill Poisioning turning AI agents into malware droppers – warns China’s National CERT
Hacking
Critical vulnerabilities expected in Check Point VPN products with active exploitation: update now
The Ghost in the Chat: how a bot that isn’t in your group steals messages from Telegram HTML exports
Japan’s Digital Agency says VPN flaw exposed 246,000 personnel records
One Router, Three Vulnerabilities: Security Research on the TOTOLINK A720R
Coast Guard and FBI boarded 2 energy tankers due to cyberattacks. How big is the risk?
Nintendo warns of Switch code execution flaw via on-screen QR codes
Hacking OpenAI
Intelligence and Information Warfare
A warning about ‘model welfare’
Investigații The Kremlin’s Digital Pirates: How Russian Tracking Pixels Harvest Romanians’ Data to Fund Conspiracies and Extremism
Skill Poisioning turning AI agents into malware droppers – warns China’s National CERT
Donald Trump rejects calls from tech bosses for an AI slowdown
China bristles at Anthropic CEO’s ‘fearmongering’ about its AI development
Red Heron exploits Gitea n-day flaw in multinational campaign, exposing new Linux rootkit
Iranian cyber targeting of dissidents, activists and journalists
SilkParasite Infrastructure: SpiceRAT Servers Tied to Energy and Government Targets Across Central Asia
Amazon’s AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage
Beware the SparroWock: The backdoor that bites, the commands that catch
Cybersecurity
Meta Failed to Catch Hundreds of AI Child Abuse Ads. Some Included Images of Real Kids
Anthropic CEO Dario Amodei says AI industry needs to give safety measures time to catch up
We Must Pace the Frontier
First notification of a personal data breach caused by an attack executed using an AI agent
Gemini Hacked Three Companies in First Known Breakout by Google’s AI
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
Pierluigi Paganini
( SecurityAffairs – hacking, newsletter )
About Author
Andy Curtis is an award-winning security consultant, researcher and public speaker. He has been working in the computer security industry since the early 1990s, having been employed by state and federal government, leading healthcare and banking providers across three continents. He has given talks about computer security for some of the world’s largest companies, worked with law enforcement agencies on investigations into hacking groups, and is a regular voice on TV and radio explaining IT security threats.
Tags: Breaking News , Cybercrime , data breach , hacking , hacking news , information security news , IT Information Security , Malware , Newsletter , Pierluigi Paganini , Security , Security Affairs , Security News
0%
Love
0%
Funny
0%
Wow
0%
Sad
0%
Angry
Post navigation



 September 20, 2026