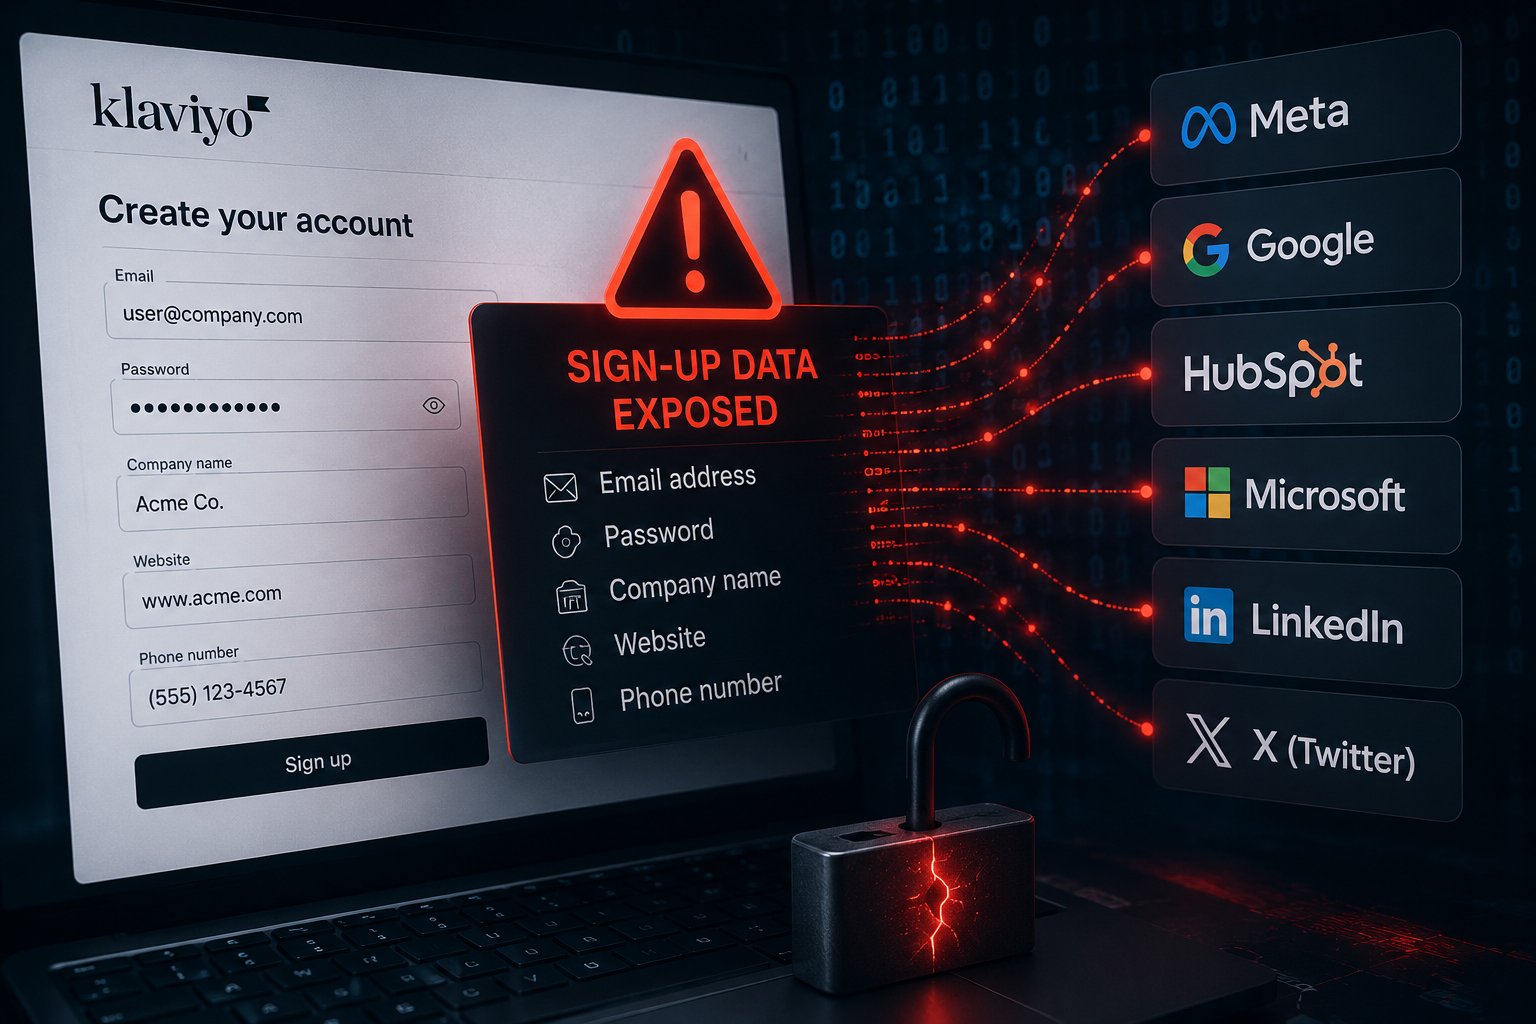
Klaviyo Sign-Up Bug May Have Exposed Passwords to Ad Trackers
Klaviyo has fixed a website configuration bug that may have exposed new customers’ sign-up data, including passwords, to third-party trackers...
Klaviyo has fixed a website configuration bug that may have exposed new customers’ sign-up data, including passwords, to third-party trackers...

Ravie LakshmananAug 10, 2026Ransomware / Cybercrime Microsoft has disclosed that Storm-1175, a financially motivated threat actor linked to China, has...

OpenAI has announced that it's pausing some "internal activities" involving its upcoming artificial intelligence (AI) model Astra after an internal...
Samsung is starting August with a security sweep that patches dozens of flaws across Galaxy phones and tablets. The company...

Ravie LakshmananAug 08, 2026Zero-Day / Vulnerability Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data...

WordPress has fixed a pre-authentication reflected cross-site scripting (XSS) flaw in its login screen that affects every version of the...
The OnePlus 10T has reached the end of its guaranteed security-support window, but that does not mean owners need to...

Swati KhandelwalAug 07, 2026Endpoint Security / Vulnerability Entra ID researcher Dirk-jan Mollema demonstrated that malware already running in a signed-in...

The Palo Alto report showed attacks that, it said, “demonstrate how malware on a compromised endpoint can misuse onboarding, recovery...
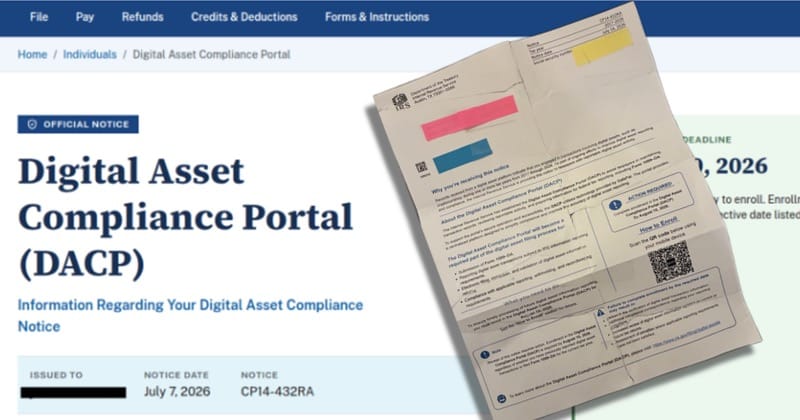
Do you hold cryptocurrency? Have you received a letter telling you that you must register with a so-called "Digital Asset...
Vulnerabilities in Car Anti-Theft Device This is disturbing: …a team of security researchers at UC San Diego, who found that...

Apple’s complaint is more detailed than that. Among many other things, it claims Tan allegedly directed job candidates still at...

A credential-stealing npm worm that first appeared in keyv@6.0.0 spread beyond the Keyv and Cacheable namespaces into hundreds of packages...

Cybersecurity researchers have disclosed details of an active, multi-wave campaign that employs social engineering lures themed around Adobe and Zoom...

The cybersecurity industry has spent decades assuming that offensive capability scales with technical expertise. That assumption is starting to break....