
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 119
This website uses cookies to improve your experience while you navigate through the website. Out of these cookies, the cookies...
 Italy ’s Parliament Under Cyber Pressure: Why the Attack on the Chamber Matters
Australia’s Cyber Spy Chief: Expect More Disruption as AI Accelerates Hacking
 CyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan Targets
 Japan, Australia, US should build a second-island-chain air bridge
 GoAhead TLS Flaws Allow Revoked Client Certificates and Enable Session Decryption
This website uses cookies to improve your experience while you navigate through the website. Out of these cookies, the cookies...

Security Affairs newsletter Round 600 by Pierluigi Paganini – INTERNATIONAL EDITION Pierluigi Paganini October 18, 2026 A new round of...

This past week, I served as the moderator for a breakout session at the Michigan Cyber Summit 2026. The session’s...
Krybit is a fast-growing ransomware gang that was hacked by a rival, hit back, and is still extorting victims. Find...

ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in...
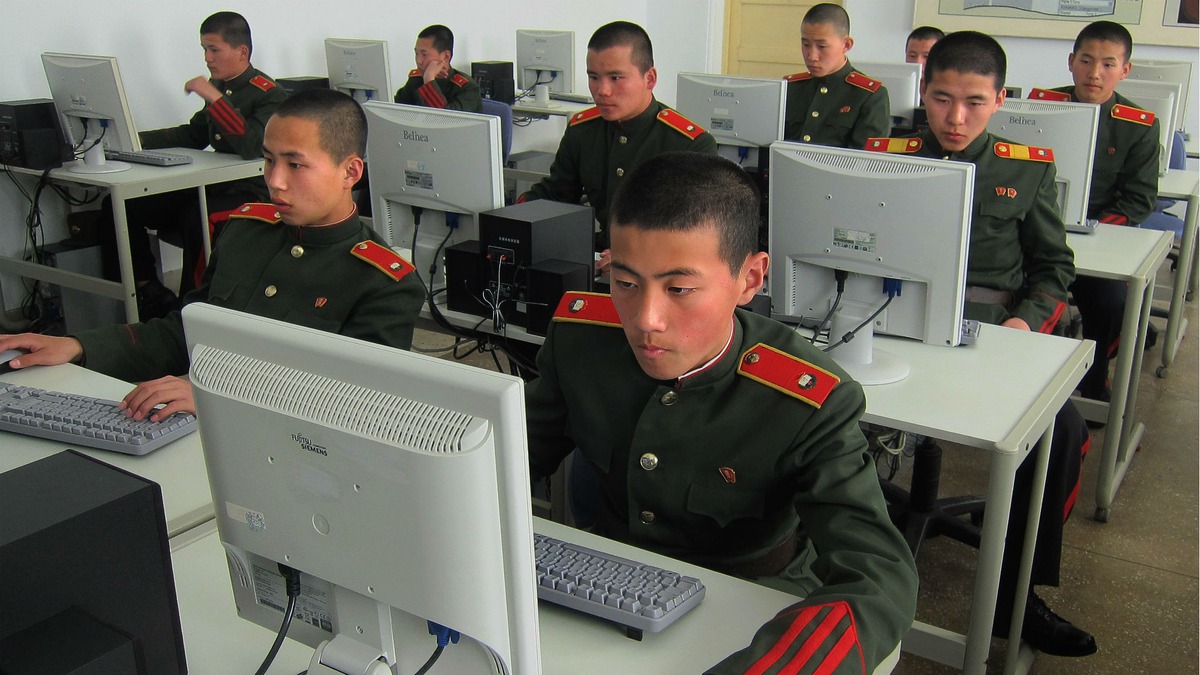
North Korean IT Workers Used Stolen US Identities to Earn $3 Million Pierluigi Paganini October 17, 2026 The FBI raided...

Canada’s planned surveillance law is the latest grim step in a series of threats to encryption that are spreading around...
Canada’s planned surveillance law is the latest grim step in a series of threats to encryption that are spreading around...
In September, reports emerged that a Virginia woman had been submerged by a flood of emails. Hundreds of automated messages...
In September, reports emerged that a Virginia woman had been submerged by a flood of emails. Hundreds of automated messages...
In September, reports emerged that a Virginia woman had been submerged by a flood of emails. Hundreds of automated messages...

U.S. CISA adds Fortinet Multiple Products and BeyondTrust Remote Support flaws to its Known Exploited Vulnerabilities catalog Pierluigi Paganini October...
BAE Systems Cyber Incident Takes US Bankruptcy Noticing Center Offline for a Week Pierluigi Paganini October 17, 2026 A cyber...
AI Agents Accessed Indian Organizations Without Authorization, CERT-In Warns Pierluigi Paganini October 17, 2026 India’s CERT-In warns AI agents accessed...

Cybersecurity researchers have discovered a malicious npm package that's part of a recently disclosed software supply chain attack campaign dubbed...