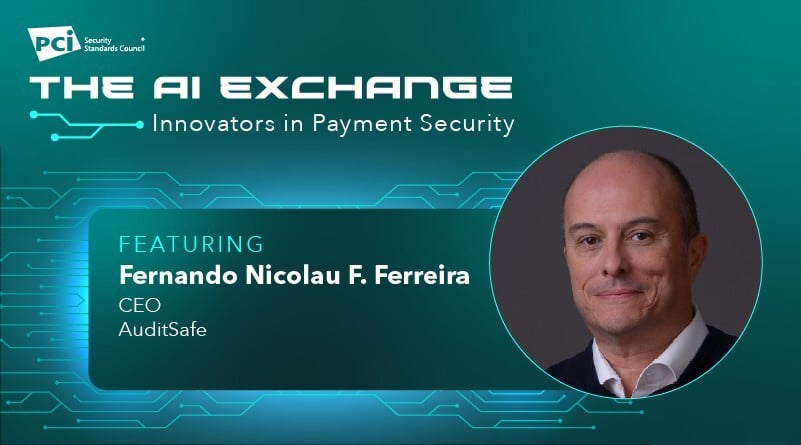
The AI Exchange: Innovators in Payment Security Featuring AuditSafe
Welcome to the PCI Security Standards Council’s blog series, The AI Exchange: Innovators in Payment Security. This special, ongoing feature of our PCI Perspectives blog offers a resource for payment security industry stakeholders to exchange information about how they are adopting and implementing artificial intelligence (AI) into their organizations.
In this edition of The AI Exchange, AuditSafe CEO, Fernando Nicolau F. Ferreira, offers insight into how his company is using AI, and how this rapidly growing technology is shaping the future of payment security.
How has your AI strategy evolved over the past 12-18 months?
Over the past 12–18 months, our approach to AI has evolved from experimentation and productivity use cases toward a more structured and governance-oriented model.
Initially, much of the focus was on understanding where AI could improve productivity, accelerate analysis, and support knowledge-intensive activities. As adoption increased, however, it became clear that the more important question was not simply where AI could be used, but how it could be used responsibly and securely.
Today, we look at AI through three interconnected lenses: business value, risk and governance, and human oversight. This is particularly important in cybersecurity and payment environments, where confidentiality, integrity, accountability, and traceability cannot be compromised in the pursuit of efficiency.
Our strategy has therefore become less about adopting individual AI tools and more about establishing the principles, controls, and governance required to use AI at scale.
What is one AI initiative that has already delivered a measurable impact within your organization, and what made it successful?
One area where we have seen clear impact is the use of AI to support knowledge-intensive and analytical activities.
AI can help professionals organize large volumes of information, identify relevant points more quickly, structure analyses, and accelerate the preparation and review of technical content. This reduces the time spent on repetitive activities and allows specialists to dedicate more attention to judgment, risk analysis, and decision-making.
The key factor behind the success of this approach has been maintaining human oversight. We do not see AI as replacing professional judgment, particularly in security, compliance, and assurance activities. Instead, we see it as an additional capability that can augment experienced professionals.
The measurable benefit is therefore not only productivity. It is also the ability to redirect human effort toward higher-value activities where context, experience, and accountability remain essential.
How are you approaching AI governance, particularly around data privacy and security?
We approach AI governance as an extension of existing risk, information security, privacy, and corporate governance disciplines rather than as an isolated technology issue. Organizations need to understand what AI systems are being used, what information is being provided to them, where that information is processed, who is accountable for their use, and what controls apply throughout the lifecycle.
From a privacy and security perspective, some fundamental principles remain unchanged: data classification, access control, least privilege, third-party risk management, secure development practices, monitoring, and incident management continue to be relevant.
What AI introduces is an additional layer of complexity. Organizations must consider issues such as inappropriate disclosure of sensitive information, model and data provenance, accuracy of AI-generated outputs, third-party dependencies, and the level of human oversight required for different decisions.
For organizations operating in the payment ecosystem, AI governance should therefore be integrated into the broader security and risk management framework rather than treated as a separate initiative.
What challenges have become more apparent as AI capabilities have matured?
One of the most significant challenges is that AI adoption can happen much faster than governance. Employees can access powerful AI capabilities almost instantly, while organizations may require considerably more time to establish policies, risk assessments, technical controls, and monitoring processes.
Another challenge is overconfidence in AI-generated results. As models become more capable and their responses more convincing, users may assume that an answer is correct simply because it appears authoritative.
Third-party risk is also becoming increasingly important. AI capabilities are being embedded into software, cloud services, cybersecurity tools, and business applications, sometimes without organizations fully recognizing the new data flows and dependencies being introduced.
The challenge is therefore not simply controlling AI. It is creating enough visibility and governance to allow organizations to benefit from AI without introducing risks that they do not understand.
What advice would you provide for an organization moving from early AI adoption to broader implementation?
My first recommendation would be: do not scale AI faster than your ability to govern it.
Organizations should establish a clear inventory of AI use cases, define ownership and accountability, classify the data that can and cannot be used, evaluate third-party risks, and determine where human oversight is mandatory.
At the same time, governance should not become a barrier to innovation. A risk-based approach is more effective than attempting to apply the same controls to every AI use case. Low-risk productivity applications and AI systems involved in sensitive data or critical decisions should not necessarily be governed in the same way.
Finally, organizations should invest in AI literacy. Policies and technology controls are important, but employees also need to understand the limitations of AI, the risks associated with sensitive information, and their own responsibility when using AI-generated outputs.
The objective should be responsible acceleration, not simply acceleration.
What AI trend (not limited to payments) are you most excited about?
I am particularly interested in the evolution from generative AI toward agentic AI. We are moving from systems that primarily generate information to systems capable of interpreting objectives, interacting with multiple sources, executing tasks, and participating in increasingly complex workflows.
This creates enormous opportunities for cybersecurity, compliance, risk management, and payment security. In the future, AI agents may continuously analyze controls, identify anomalies, correlate evidence, support risk assessments, and help organizations respond more quickly to changes in their environment.
At the same time, agentic AI makes governance even more important. The greater the autonomy given to an AI system, the more important identity, authorization, segregation of duties, monitoring, traceability, and human accountability become.
For me, this combination of increased capability and increased governance responsibility is one of the most important developments we will see in the next few years.

About Author